
NAT Compatibility
To establish a direct connection between an external user device and the session host, HDX™ Direct leverages hole punching for NAT traversal and STUN to facilitate the exchange of the public IP address and port mappings for the client device and session host. This is similar to how VoIP, unified communications, and P2P solutions work.
As long as firewalls and other network components are configured to allow the UDP traffic for the STUN requests and the HDX sessions, HDX Direct for external users is expected to work. However, there are certain scenarios where the NAT types of the user and session host networks lead to an incompatible combination, thus causing HDX Direct to fail.
Validations
You can validate the NAT type and filtering on the client and the session host by using STUNTMAN’s STUN client utility:
-
Download the appropriate package for the target platform from stunprotocol.org, and extract the contents.
-
Open a terminal prompt and navigate to the directory where the contents were extracted.
-
Run the following command:
.\stunclient.exe stunserver2024.stunprotocol.org --mode behavior -
Take note of the output.If the binding and behavior tests are successful, both binding test and behavior test report the success and a NAT behavior is specified:
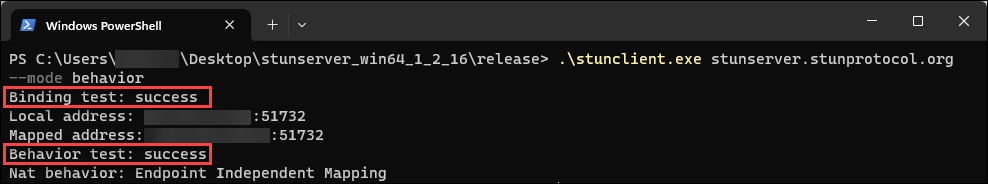 If the tests fail, binding test and/or behavior test report the failure.
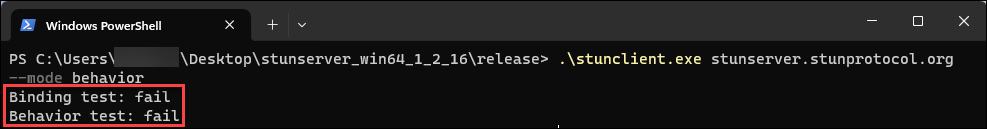
-
Run the following command:
.\stunclient.exe stunserver2024.stunprotocol.org --mode filtering -
Take note of the output.
See the following table to determine if HDX Direct for external users is expected to work based on the test results of both the client and session host:
| Client NAT Behavior | Client NAT Filtering | Session Host NAT Behavior | Session Host NAT Filtering | Expected to work? |
|---|---|---|---|---|
| Endpoint Independent Mapping | Any | Endpoint Independent Mapping | Any | Yes |
| Endpoint Independent Mapping | Endpoint Independent Filtering | Address Dedependent Mapping | Any | Yes |
| Endpoint Independent Mapping | Address Dependent Filtering | Address Dedependent Mapping | Any | No |
| Endpoint Independent Mapping | Address and Port Dependent Filtering | Address Dedependent Mapping | Any | No |
| Endpoint Independent Mapping | Endpoint Independent Filtering | Address and Port Dedependent Mapping | Endpoint Independent Filtering | Yes |
| Endpoint Independent Mapping | Address Dependent Filtering | Address Dedependent Mapping | Any | No |
| Endpoint Independent Mapping | Address and Port Dependent Filtering | Address Dedependent Mapping | Any | No |
| Address Dependent Mapping | Any | Endpoint Independent Mapping | Endpoint Independent Filtering | Yes |
| Address Dependent Mapping | Any | Endpoint Independent Mapping | Address Dependent Filtering | No |
| Address Dependent Mapping | Any | Endpoint Independent Mapping | Address and Port Dependent Filtering | No |
| Address Dependent Mapping | Any | Address Dependent Mapping | Any | No |
| Address Dependent Mapping | Any | Address and Port Dependent Mapping | Any | No |
| Address and Port Dependent Mapping | Any | Endpoint Independent Mapping | Endpoint Independent Filtering | Yes |
| Address and Port Dependent Mapping | Any | Endpoint Independent Mapping | Address Dependent Filtering | No |
| Address and Port Dependent Mapping | Any | Endpoint Independent Mapping | Address and Port Dependent Filtering | No |
| Address and Port Dependent Mapping | Any | Address Dependent Mapping | Any | No |
| Address and Port Dependent Mapping | Any | Address and Port Dependent Mapping | Any | No |
| Fail | Any | Any | Any | No |
| Any | Any | Fail | Any | No |
| Fail | Any | Fail | Any | No |