
Secure HDX
macOS VDA support Secure HDX
The Secure HDX Feature evolves from the original Secure ICA. The main drawback of the original Secure ICA was its susceptibility to MITM attacks, which Secure HDX addresses. In addition, the up-to-date Advanced Encryption Standard (AES) cipher is used. One key aspect of Secure HDX vs. network-level encryption (TLS or DTLS) is the ability to provide true end-to-end encryption (E2EE) between the Citrix Workspace App (CWA) and the VDA. This means that no intermediate network elements (including the Citrix Gateway) are able to decrypt the ICA traffic.
| Phase | Algorithm |
|---|---|
| key exchange | ECDHE |
| authentication | RSA |
| session cipher | AES-256 |
| cipher-block dependency and additional options | GCM |
| message authentication | SHA256 |
Network encryption consideration
Network level encryption and Secure HDX are complementary: customers can choose to enable both simultaneously.
Feature toggle/Group policy
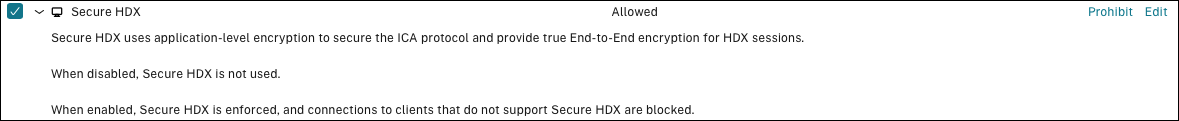
The feature toggle Secure HDX policy, is designed to turn on/off this feature.
Backward compatibility & limitation
Capability negotiation is performed during the ICA® initialization phase, so this feature is compatible with old versions; macOS VDA does not support "Shield" at the moment, so currently we support “non-Shield” scenarios. In “non-Shield” mode, VDA self-signed certificate is provided to CWA via a trusted path, while in “Shield” mode, VDA self-signed certificate is provided to CWA via CLXMTP protocol.