-
Apps configuration and management
-
Citrix Enterprise Browser to Chrome Enterprise Premium migration
This content has been machine translated dynamically.
Dieser Inhalt ist eine maschinelle Übersetzung, die dynamisch erstellt wurde. (Haftungsausschluss)
Cet article a été traduit automatiquement de manière dynamique. (Clause de non responsabilité)
Este artículo lo ha traducido una máquina de forma dinámica. (Aviso legal)
此内容已经过机器动态翻译。 放弃
このコンテンツは動的に機械翻訳されています。免責事項
이 콘텐츠는 동적으로 기계 번역되었습니다. 책임 부인
Este texto foi traduzido automaticamente. (Aviso legal)
Questo contenuto è stato tradotto dinamicamente con traduzione automatica.(Esclusione di responsabilità))
This article has been machine translated.
Dieser Artikel wurde maschinell übersetzt. (Haftungsausschluss)
Ce article a été traduit automatiquement. (Clause de non responsabilité)
Este artículo ha sido traducido automáticamente. (Aviso legal)
この記事は機械翻訳されています.免責事項
이 기사는 기계 번역되었습니다.책임 부인
Este artigo foi traduzido automaticamente.(Aviso legal)
这篇文章已经过机器翻译.放弃
Questo articolo è stato tradotto automaticamente.(Esclusione di responsabilità))
Translation failed!
Access mode-based policy enforcement
Access mode-based policy enforcement lets administrators restrict how a user connects to an application. The connection can be through a browser-based client or the Citrix Secure Access client. Previously, Secure Private Access had no way to restrict access based on which a client initiates the session. Access mode adds that capability.
For example, administrators can configure that SSH and RDP applications are only reachable through a browser, such as Chrome Enterprise Premium, and not tunneled through the Citrix Secure Access client. This ensures that browser-based security controls always apply.
Note:
Access mode is a restricting condition only. It can narrow down the access but cannot grant access on its own. All other conditions in the policy are still evaluated.
How it works
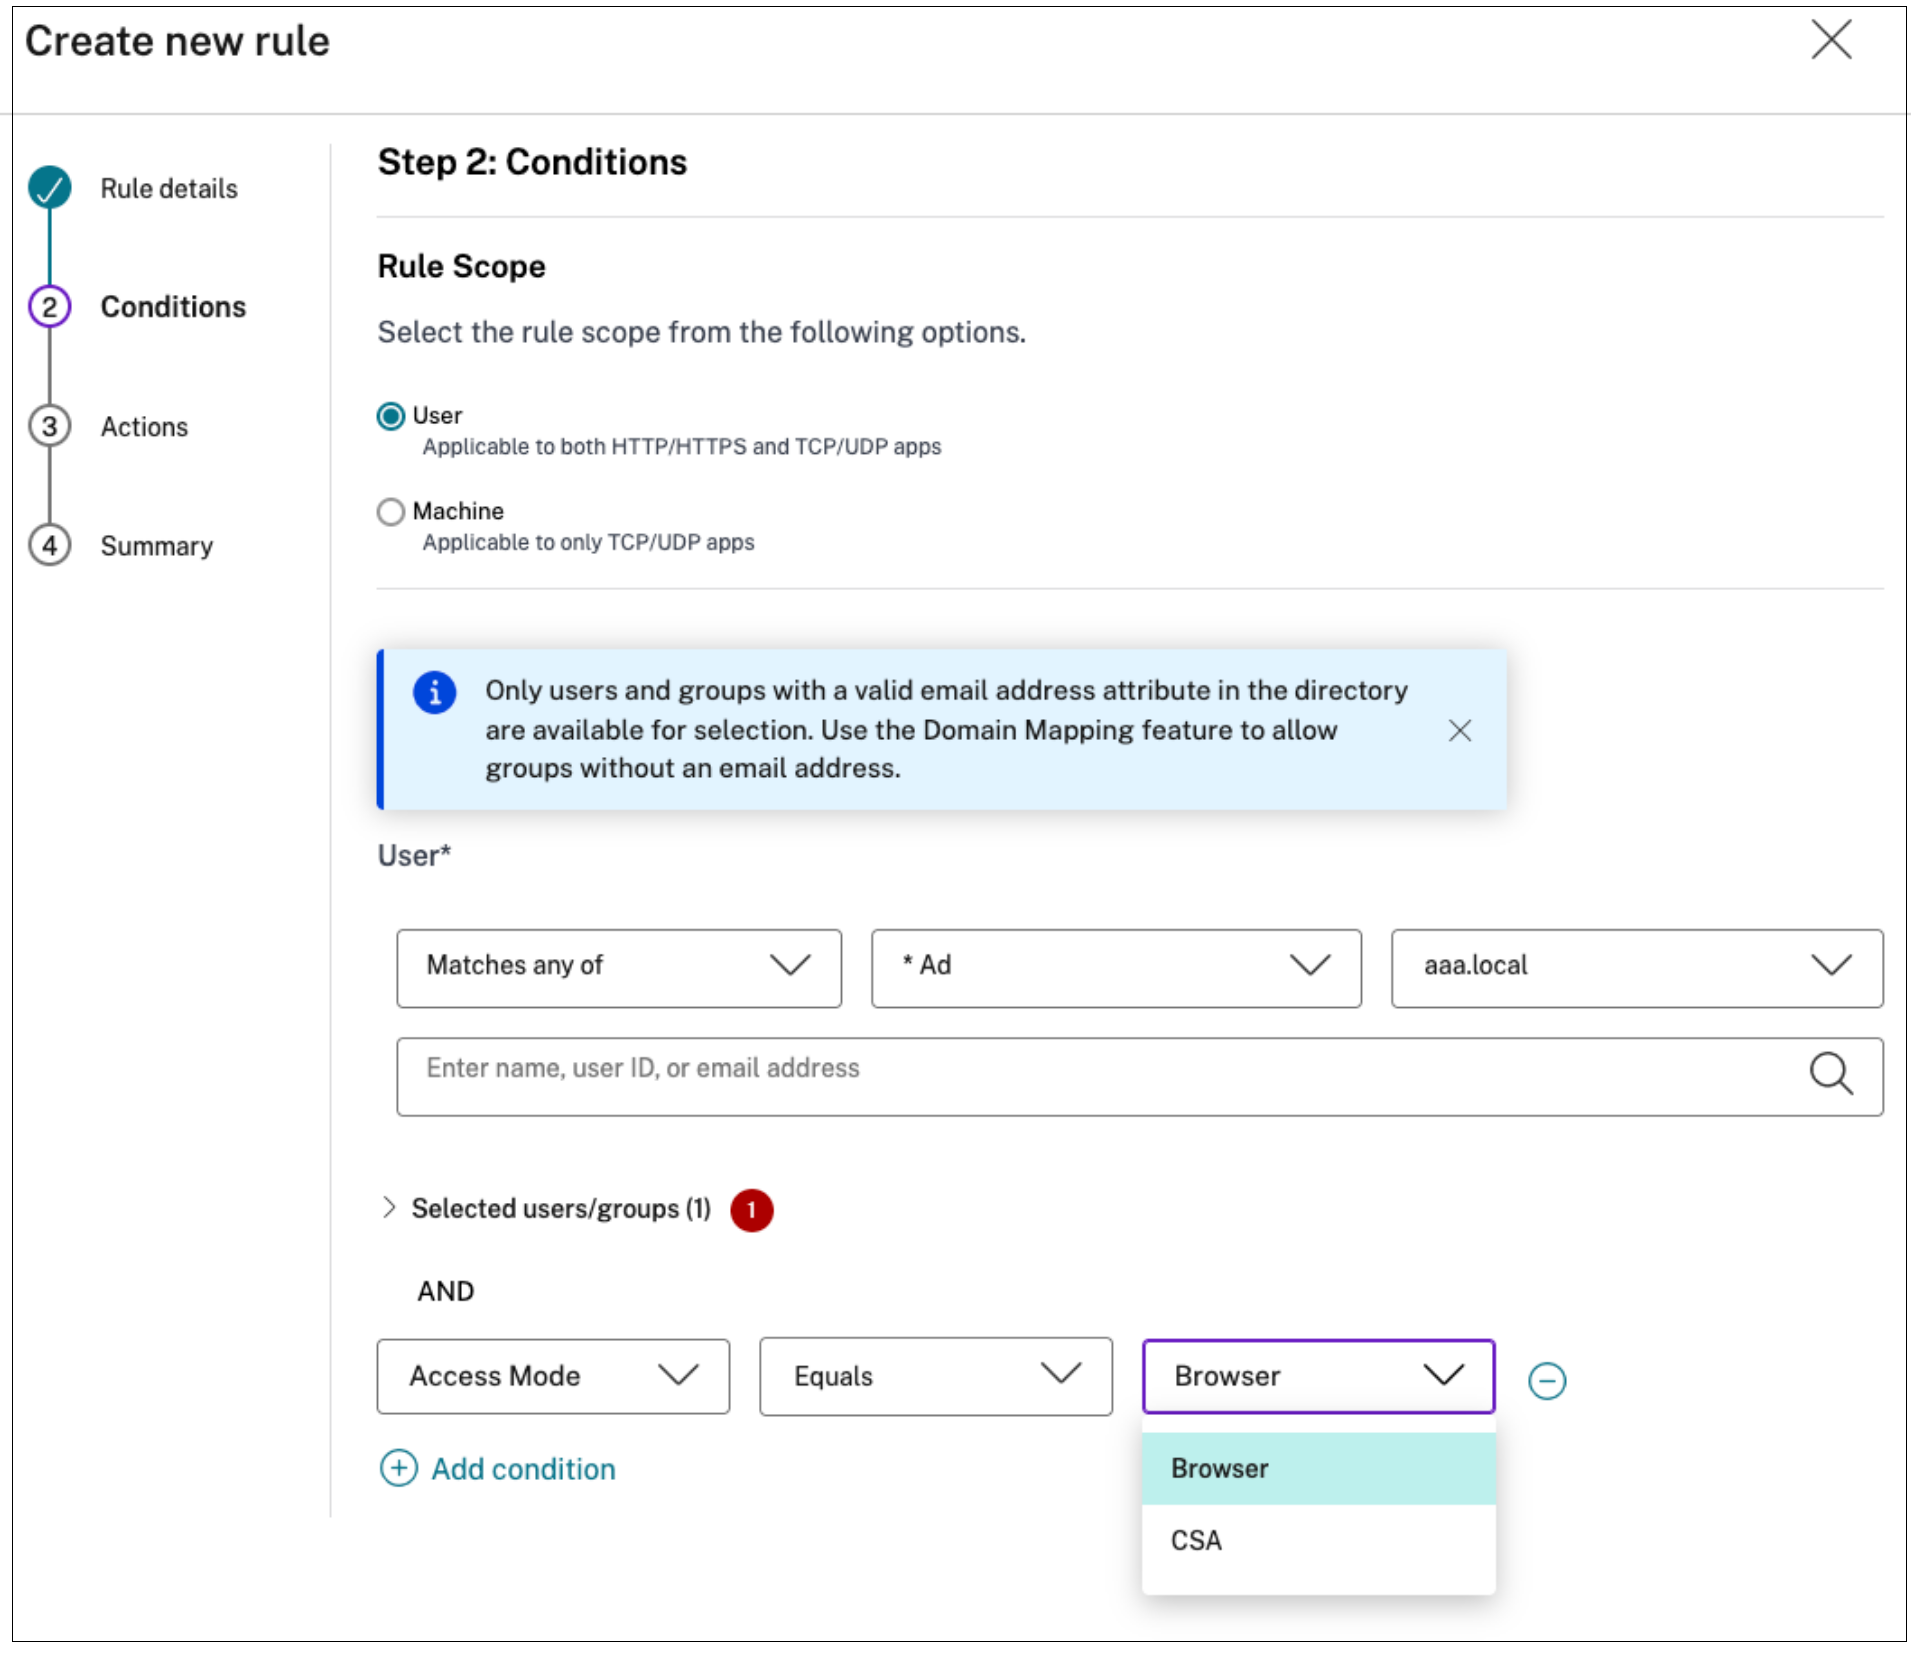
Access mode is configured in the Secure Private Access admin console and can be added to a rule in any of the three policy types.
The following figure displays a sample acess policy rule condition.
End-user experience
Based on the access mode, application enumeration and launch are either allowed or restricted.
- Matching client — The application is enumerated and launches normally.
- Non-matching client — The application is not shown in the app list during enumeration, and a launch attempt is blocked. The user is sent to the standard access-denied page. No new denial message is introduced.
- Undeterminable session — When the access mode cannot be determined (for example, some mobile Secure Access sessions), the access mode condition is skipped and the session is unaffected. All other conditions still apply.
Share
Share
In this article
This Preview product documentation is Citrix Confidential.
You agree to hold this documentation confidential pursuant to the terms of your Citrix Beta/Tech Preview Agreement.
The development, release and timing of any features or functionality described in the Preview documentation remains at our sole discretion and are subject to change without notice or consultation.
The documentation is for informational purposes only and is not a commitment, promise or legal obligation to deliver any material, code or functionality and should not be relied upon in making Citrix product purchase decisions.
If you do not agree, select I DO NOT AGREE to exit.